Anti-DDoS infrastructure
OVHcloud Anti-DDoS infrastructure protects against bad actors
Every OVHcloud product includes Anti-DDoS protection by default, mitigating attacks at multi-terabit-per-second scale.
Fine-tune your protection per workload with Anti-DDoS Profiling.
Simple and smart
All OVHcloud products are delivered with Anti-DDoS protection enabled. If you have additional requirements, you can customize protection rules via the control panel, now tunable per workload with Anti-DDoS Profiling.
Global existence
OVHcloud operates its own large distributed global network that provides enough throughput to mitigate attacks no matter where they originate. This is how we are able to provide seamless service to customers even during an active attack.
Savings
No matter the size of your project from a personal blog to a full-scale cloud infrastructure, all benefit from anti-DDoS protection at no additional cost. No longer do you need to scale up your workloads to maintain QoS during an attack, mitigation is enabled in seconds.
Get the best of our Anti-DDoS infrastructure
OVHcloud Anti-DDoS is composed of:
- Multi-Tbps capacity for global attack filtering
- Always-on attack detection and fast mitigation of malicious traffic
- Unmetered and no additional cost, regardless of the volume of attack
- No time limit on protection. It lasts the full duration of a DDoS attack
Our infrastructure also benefits from:
- Vast experience in protecting a range of services, from small web servers, DNS services to large web hosting farms or cloud platforms
- High performance thanks to best-in-class hardware and software solutions
- Data Sovereignty, so your traffic is not shared with external parties
- True customisation for meeting your needs and tuning components
DDoS attack mitigation guidelines
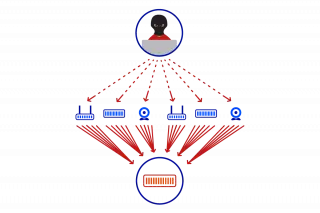
Are you prepared for a DDoS attack? Be proactive and set up special Edge Network Firewall rules to offload your server's iptables for the duration of an attack. Through our guide, learn how to prepare for a botnet attack, what to observe and which services to place more attention on.
Multi-layered (or multi staging) defense system
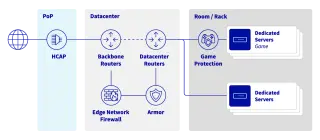
To ensure the best quality of network traffic filtration with minimal added latency for your services, we sliced every mitigation node into a few stages. Every part is responsible for a particular task and implements different logic. We use the latest hardware and software innovations in the industry to assure that we are on top of our game.
Elevate your protection with Network Security Dashboard
With provided observability you get immediate insigts and control on how your public IP services are being protected from network attacks by OVHcloud's network defense systems.
- Centralized: access directly from your Control Panel and get immediate insights for your network protection.
- Advanced monitoring tools: the dashboard provides comprehensive Anti-DDoS activity logs, dynamic traffic charts, and statistics for a complete security overview.
Tune protection to your workload
New profiling options let you better protect network-intensive workloads from network attacks. Apply an application-aware profile and a sensitivity to your IPs and your mitigation is tuned to how your service actually behaves — stronger protection, with fewer false positives on legitimate, bursty traffic. It refines your mitigation, never replaces it: disable it and your IP returns to the default protection. Self-service, from your Control Panel.

Application-layer protections
In some cases, generic protection may not be enough. This is especially true in web and gaming areas, which are often subject to application attacks. In such circumstances, application-layer logic is being exploited by attackers which makes these threats invisible to general firewalls. OVHcloud offers a number of products that can help you secure your services.
Ready to get started?
Create an account and launch your services in minutes.
Choose the right protection for your needs
FAQ
What kind of attacks does the Anti-DDoS Infrastructure protect me from?
Cyber security covers a broad range of threats and a network attack (or attack vector) combines many factors and may differ across time as well as can be vendor-specific. Our Anti-DDoS Infrastructure addresses the greatest of those: Distributed Denial-of-Service attacks, packet floods (incl. syn flood), spoofing, malformed or amplification attacks, etc. Most of these you can't filter on your own as they can saturate the network link in front of your server.
Which OVHcloud products are protected?
Each and every OVHcloud product and solution is protected. Protection is at the edge of our network and also inside our backbone network. In this manner, everything exposed from the OVHcloud network to the outside world is protected.
Why is OVHcloud Anti-DDoS Infrastructure needed for my server?
The likelihood of becoming the target of a DDoS attack is high and a very common occurrence. With OVHcloud anti-DDoS protection, you can protect your services against these types of threats, and ensure that your web users do not experience any issues like slow browsing or inaccessible pages.
Will I pay extra if I come under a large attack?
No, OVHcloud's Anti-DDoS Infrastructure is unmetered, which means we are not billing bandwidth. In addition, protection is built into the price of our products.
Am I protected even after "mitigation is disabled"?
Yes, our system has always-on detection. If anything suspicious is detected, then the traffic goes under "mitigation" which means deeper analysis is enabled and filtering may occur. When mitigation is disabled, all returns to the normal state and the system remains ready to mitigate any attacker's activities.
Can I tune Anti-DDoS to my workload?
Yes. New Anti-DDoS Profiling options let you apply an application-aware profile and a sensitivity to your public IPs to better protect network-intensive workloads — for example VPN, blockchain or gaming — with fewer false positives on legitimate traffic. Self-service, from your Control Panel.
Does Profiling change my current protection?
No. It only refines the mitigation for the workloads you describe; every other attack vector is handled exactly as today, and disabling a policy returns the IP to the default protection.
Is there a limit to the number of attacks per month that may be mitigated?
There is no limit for receiving protection, regardless of how many times your services are targeted by DDoS attacks.
Will the anti-DDoS solution stop working if the attack exceeds a set traffic threshold (in GB/s)?
We do not apply any limits in terms of traffic, even if the attacks are of high volume.
What is the VAC?
The VAC is a principal part of our Anti-DDoS Infrastructure and is a combination of different technologies constantly being developed by OVHcloud, and designed to mitigate DDoS attacks. VAC can filter incoming traffic so that only legitimate data packets pass through and reach your server, while illegitimate traffic is blocked. Notably, VAC includes an Edge Network Firewall and Armor components.
What does it mean if I observe entries in the 'Scrubbing Centre Activity Log?
Since years, OVHcloud offers an Anti-DDoS system to protect your public IP addresses. Recently, you can review such events directly in your Control Panel. The Scrubbing Centre log is where you can find record of all detected suspicious activities. And for the most recent events, you also have the option to view related traffic charts.
I don't see any entries in the Scrubbing Center log, is this normal?
Yes, that's good! That means we haven't seen any suspected attacks targeting your public IP addresses.
Why I don't see traffic charts or logs for the public IP addresses I entered?
Such data is available only for Public IP addresses during automatic Anti-DDoS Infrastructure detection event (when traffic is redirected via the Scrubbing Center for deeper analysis or cleaning)
Why am I unable to view traffic charts for certain entries in the Scrubbing Center log?
Please note that traffic chart data is available only for the last 2 weeks, while we keep logs available for a period of 1 year.